Hashtag
Follow #iso21434#iso21434
2 public posts
- There has been a lot of noise after the recent AIS 189 updates from ARAI. Instead of adding to the confusion, I thought it would be more useful to step back and look at AIS 189 from a practical engineering and compliance perspective. For OEMs, Tier-1 suppliers, partners, and leadership teams, the real question is not whether AIS 189 creates more work. It does. The better question is: How much of this work can be built on top of an existing ISO/SAE 21434 cybersecurity engineering framework? That is the approach I have taken in this article. The intent is to break down AIS 189 in a way that helps organisations understand what can be reused, what needs to be updated, and what needs to be built specifically for the Indian type-approval context. If your organisation has already invested in ISO/SAE 21434, you are not starting from zero. But you do need to understand the regulatory delta clearly especially around CSMS certification, annual reporting, supplier dependencies, cryptographic justification, forensic logging, modification control, and evidence retention. I would be very interested in feedback from OEMs, Tier-1s, testing agencies, cybersecurity teams, and compliance leaders working through this transition. Have a look and share your thoughts. https://sumitchouhan.com/articles/iso-21434-ais-189 #AIS189 #ISO21434 #AutomotiveCybersecurity #CSMS #TARA #VehicleCybersecurity #ConnectedVehicles #TypeApproval #ARAI #IndiaAutomotive #CyberSecurity
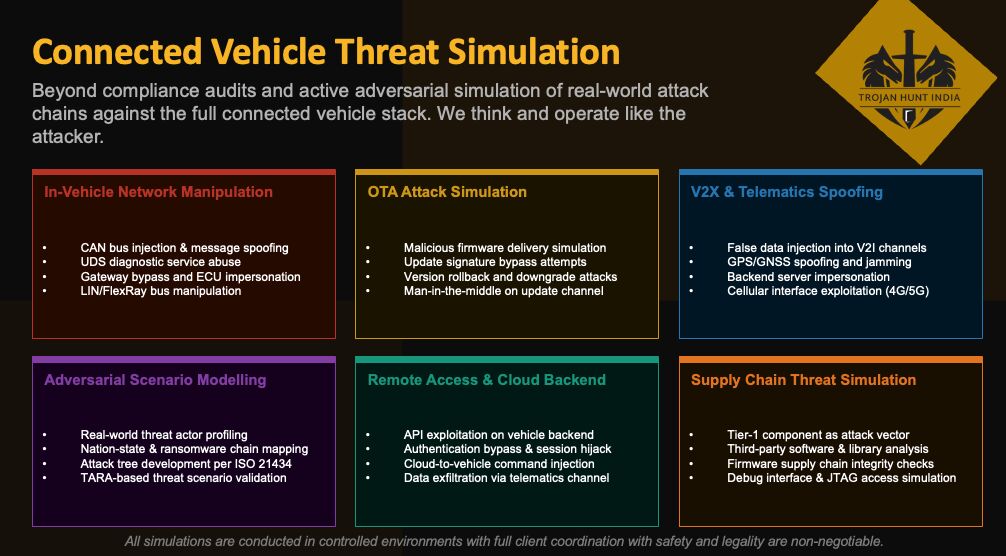
- Most automotive hashtag#cybersecurity conversations still revolve around one thing - compliance. Pass the audit. Close the findings and move on. And everyone feels good. Until something actually breaks. Attackers don’t care about your audit report. They don’t look at controls in isolation. They look at how everything connects and more importantly, where it doesn’t hold together. That’s exactly where most vehicle programs are still weak. This is where hashtag#ConnectedVehicle hashtag#ThreatSimulation changes the game. This is not another checklist and definitely not another “ISO-aligned assessment”. But actually asking: 1. What happens if someone injects messages inside the vehicle network and pivots through the gateway? 2. What happens when OTA isn’t broken at the crypto layer, but at rollback logic? 3. What happens when V2X data is technically valid… but completely false? 4. What happens when your backend becomes the attack path into the vehicle? Because that’s how real attacks work as chains, not events. and The uncomfortable truth? You can be fully aligned to ISO 21434… and still be vulnerable in production. Standards give you structure. They don’t guarantee resilience. If we don’t start validating vehicles the way attackers think, we’re just building confidence… not security. Reach us today on [email protected] for more information. For hashtag#UAE and other global clients reach us on [email protected] Trojan Hunt India LLP Trojan Hunt International FZ LLC #AutomotiveCybersecurity #ConnectedVehicles #ISO21434 #CyberResilience #VehicleSecurity
Liked by Bhushan Chandekar
1 reactions